
NEW:ASD Essentials released 15 October 2026
The New ASD Essentials: Beyond Essential Eight
A Canberra breakfast briefing for government cybersecurity and ICT leaders.
- Tuesday 17 November 2026
- 7:30am to 10:00am
- The Boat House, Barton
Limited places · Attendance subject to confirmation · RSVP by 10 November
With speakers from the Australian Institute of Insider Threats and FirstWave
The New ASD Essentials are here. Can your agency prove its security controls actually work?
On 17 November, FirstWave and Qirx are bringing together a select group of senior government cybersecurity and ICT professionals in Canberra to discuss three important questions:
- Where are we still exposed?
- Can we demonstrate our existing security investments are reducing risk?
- What should we prioritise over the next 90 days?
Join experts from the Australian Institute of Insider Threats and FirstWave for a focused discussion on protecting critical systems, identifying blind spots and strengthening cyber resilience.
17 November · 7:30am to 10:00am · The Boat House, Barton
Places are limited, with priority given to government security professionals who influence or make cybersecurity decisions.
- Date
- Tuesday 17 November 2026
- Time
- 7:30am to 10:00am
- Venue
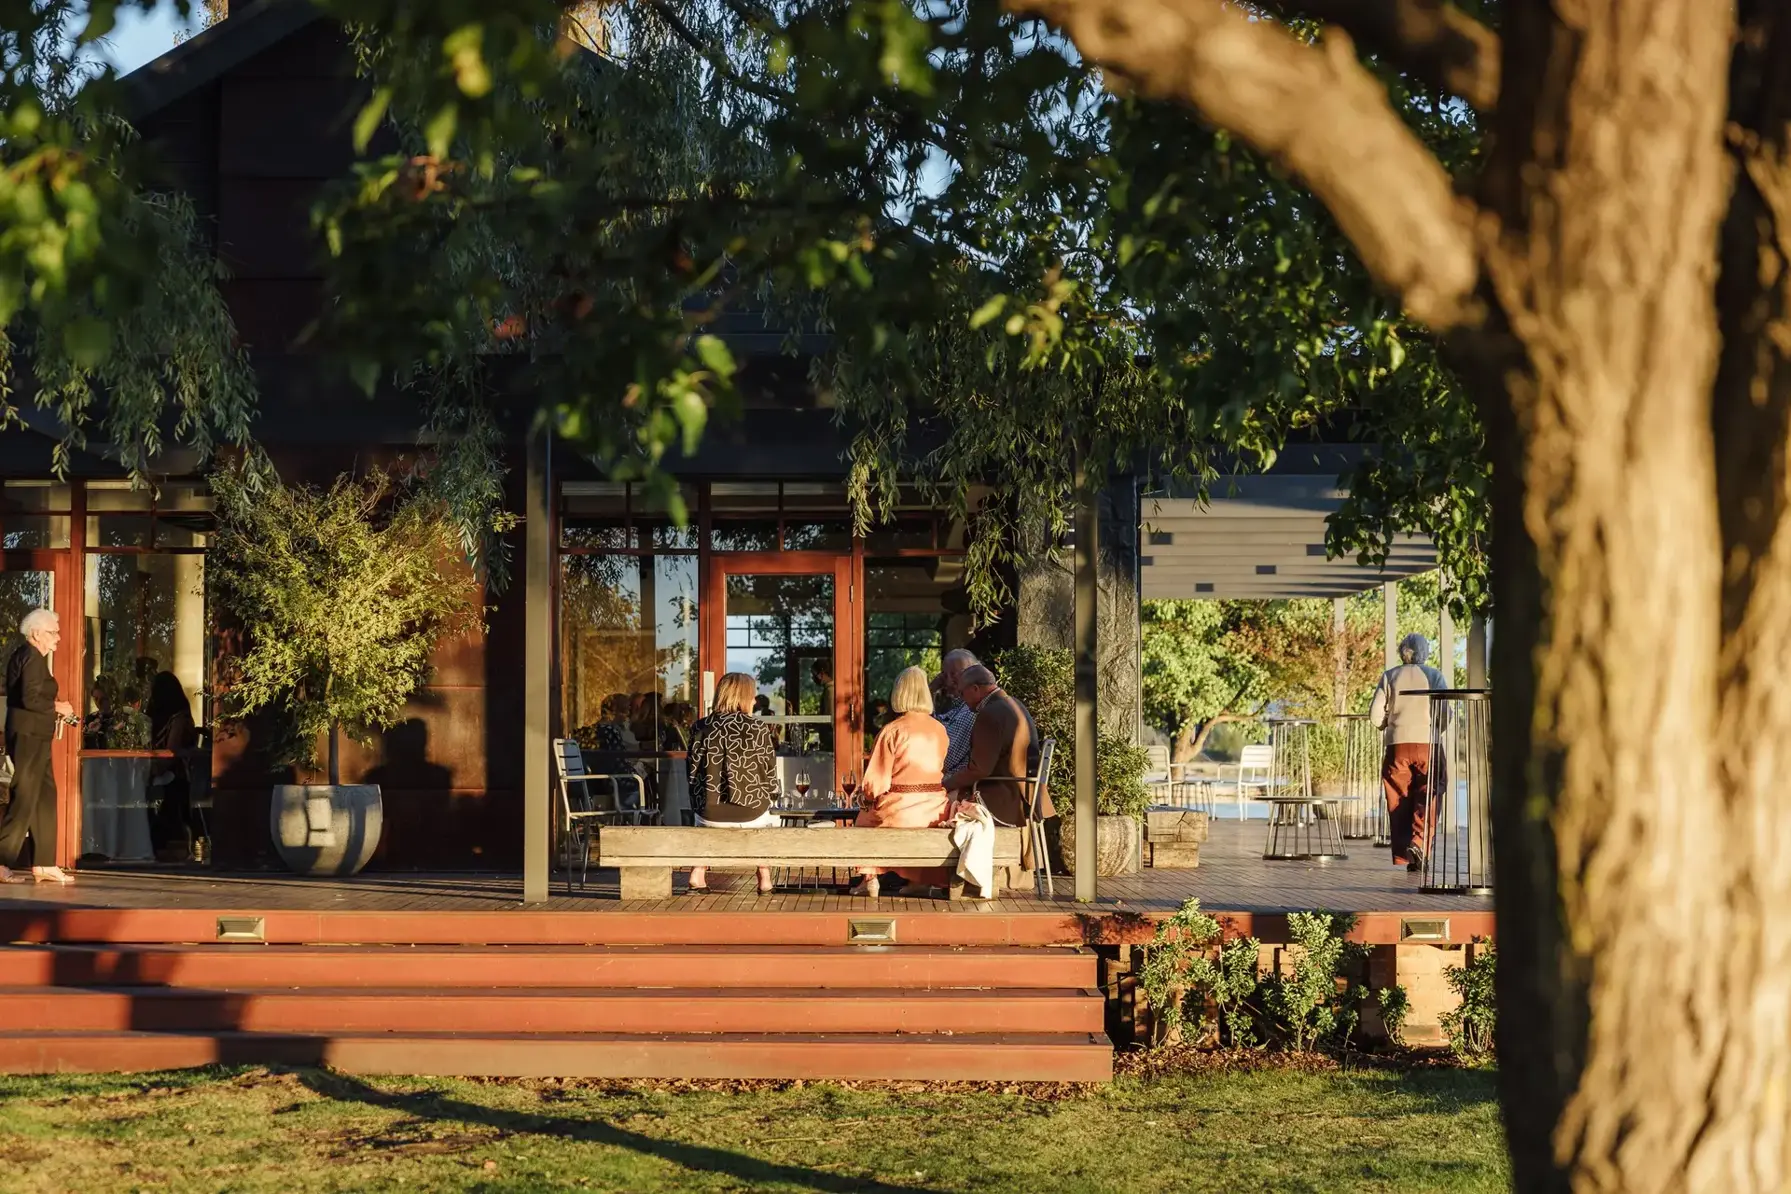
- The Boat House
- Grevillea Park, 7 Menindee Drive, Barton ACT 2600
- Parking
- Free on site
Who you'll hear from
Australian Institute of Insider Threats
Panel
Boaz Fischer
Founder
Understanding how insider threats and human behaviour can undermine security assumptions, expose vulnerabilities and influence organisational cyber resilience.
Boaz Fischer on LinkedIn (opens in a new tab)FirstWave
Panel
Greg Maren
Global Alliances Director
Understanding evolving email-borne cyber threats, the security gaps traditional defences may overlook, and practical approaches to strengthening protection against sophisticated attacks.
Greg Maren on LinkedIn (opens in a new tab)FirstWave
Host
Sharon Hunneybell
VP of Product
Chair of the Gold Coast Innovation Hub, member of the Queensland Government's Innovation Advisory Council and Industry Fellow at Griffith University. One of the AFR's 100 Women of Influence.
Sharon Hunneybell on LinkedIn (opens in a new tab)
Limited places · Attendance subject to confirmation · RSVP by 10 November
What you'll take away
Understand the new ASD Essentials. Build on existing investments. Demonstrate stronger security outcomes.
The new ASD Essentials introduces a broader approach to cybersecurity built around security principles, actions, domains and evidence of effectiveness. Join us to explore what this means for your existing security program and how to translate the guidance into practical improvements.
- Understand what has changed. Explore how ASD Essentials builds on the Essential Eight and introduces a broader, threat-informed approach to cybersecurity.
- Protect existing investments. Understand how current Essential Eight controls and security investments can contribute to the new framework, and where additional improvements may be required.
- Understand your security exposure. Explore how environmental visibility, evolving email-borne attacks and insider threats expose gaps in traditional security approaches.
- Demonstrate control effectiveness. Examine how organisations can validate security controls, identify gaps and use credible evidence to support better security decisions.
- Prioritise your next steps. Consider how Modern Defensible Architecture, assume-breach thinking and the new ASD Essentials can inform practical cybersecurity improvements.
Every attendee will receive an ASD Essentials Transition & Readiness Checklist, designed to help security teams review existing controls, identify potential gaps and prioritise practical steps towards stronger cyber resilience.
How the morning runs
- 7:30am
Breakfast and introductions
Registration and breakfast with government security peers and the speakers.
- Until 9:15am
Formal program
Keynote and expert panel exploring:
- The new ASD Essentials and implications for government cybersecurity programs
- Modern Defensible Architecture and assume-breach thinking
- Insider threats and human behaviour
- Evolving email-borne cyber threats and security blind spots
- Practical steps to strengthen security controls and cyber resilience
- 9:15am to 10:00am
Open discussion
Continue the conversation with the speakers and government security peers.
Request a seat
A focused briefing for government cybersecurity and ICT professionals.
Attendance is intended for CISOs, security managers, architects, security operations leaders, risk and governance professionals, and senior ICT staff who are responsible for or influence cybersecurity decisions.
To keep the discussion useful, places are limited and we review each request to get the right mix of government security professionals.
Tuesday 17 November 20267:30am to 10:00amThe Boat House, Barton