Know what's on your network. Including the devices nobody gave you a login for.
Open-AudIT 7 finds the devices you didn't know about, audits the ones you manage, uses AI to match their software to known vulnerabilities and checks them against ISO 27001 and the DISA STIGs.
Enterprise · free for your first 30 days. The full product and unlimited devices from day one. When the trial ends, Free keeps working on up to 100 devices.
You have a working inventory before anyone hands over a password. The devices nobody gave you a login for, from the PLC on the production line to the controller inside a server, show up on the first scan, with the evidence for each identification kept in the log.
Credentialed auditEvery edition
Add credentials and the inventory fills in: hardware down to disks and memory, every installed package and service, every network card, address and open port. Windows, Linux, Unix and network gear are all covered.
Inventory and change detectionEvery edition
Each audit is compared with the last, so a new disk, a removed package or an unexpected service is recorded as a change rather than lost in a snapshot. Export the lot as CSV, XML or JSON.
Network and application mappingEnterprise
Before a change window, see what a switch, server or database actually carries. The network is drawn from the router to the device on each port, and each application is modelled as its real servers and databases, so "which applications does this server carry?" has an answer.
Benchmarking against published standardsEnterprise
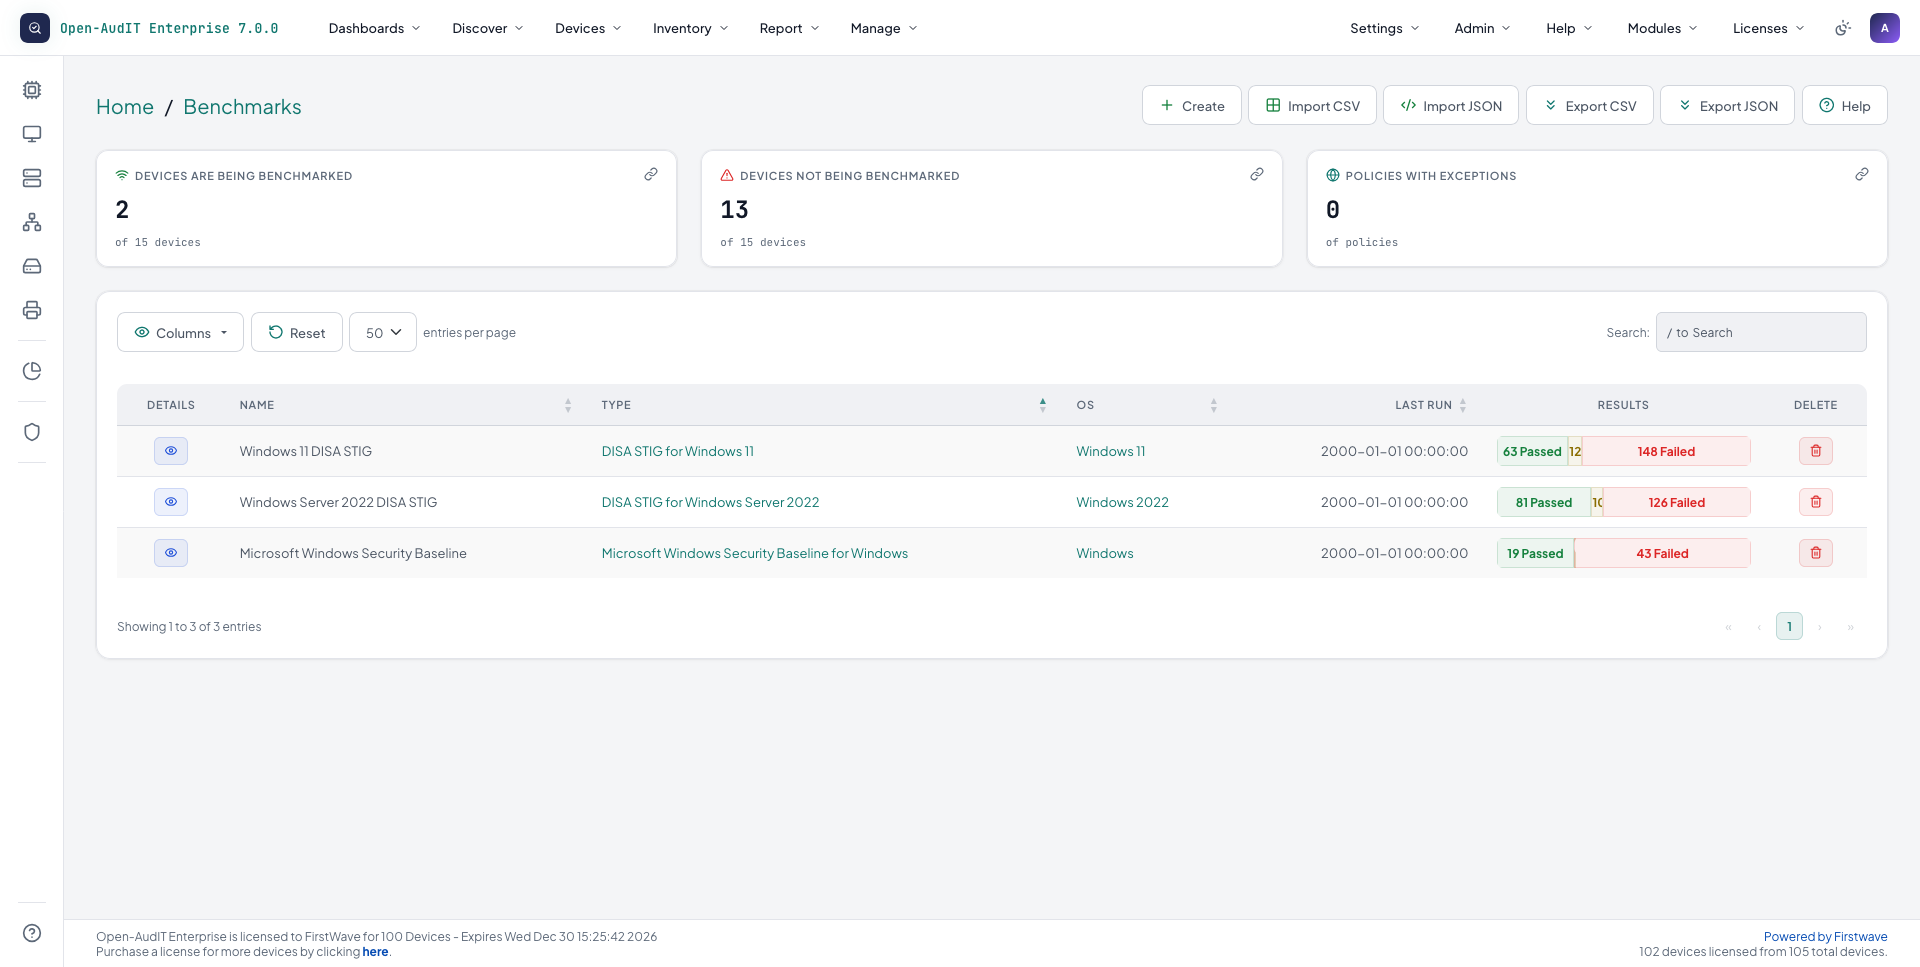
Find out whether a server is configured the way your auditor expects before the audit does. Linux is checked against CIS, DISA STIG, NIST 800-171 and the Essential Eight, and Windows and Active Directory against the DISA STIGs. Each rule is graded by severity and marked pass or fail.
Directories and peopleEnterprise
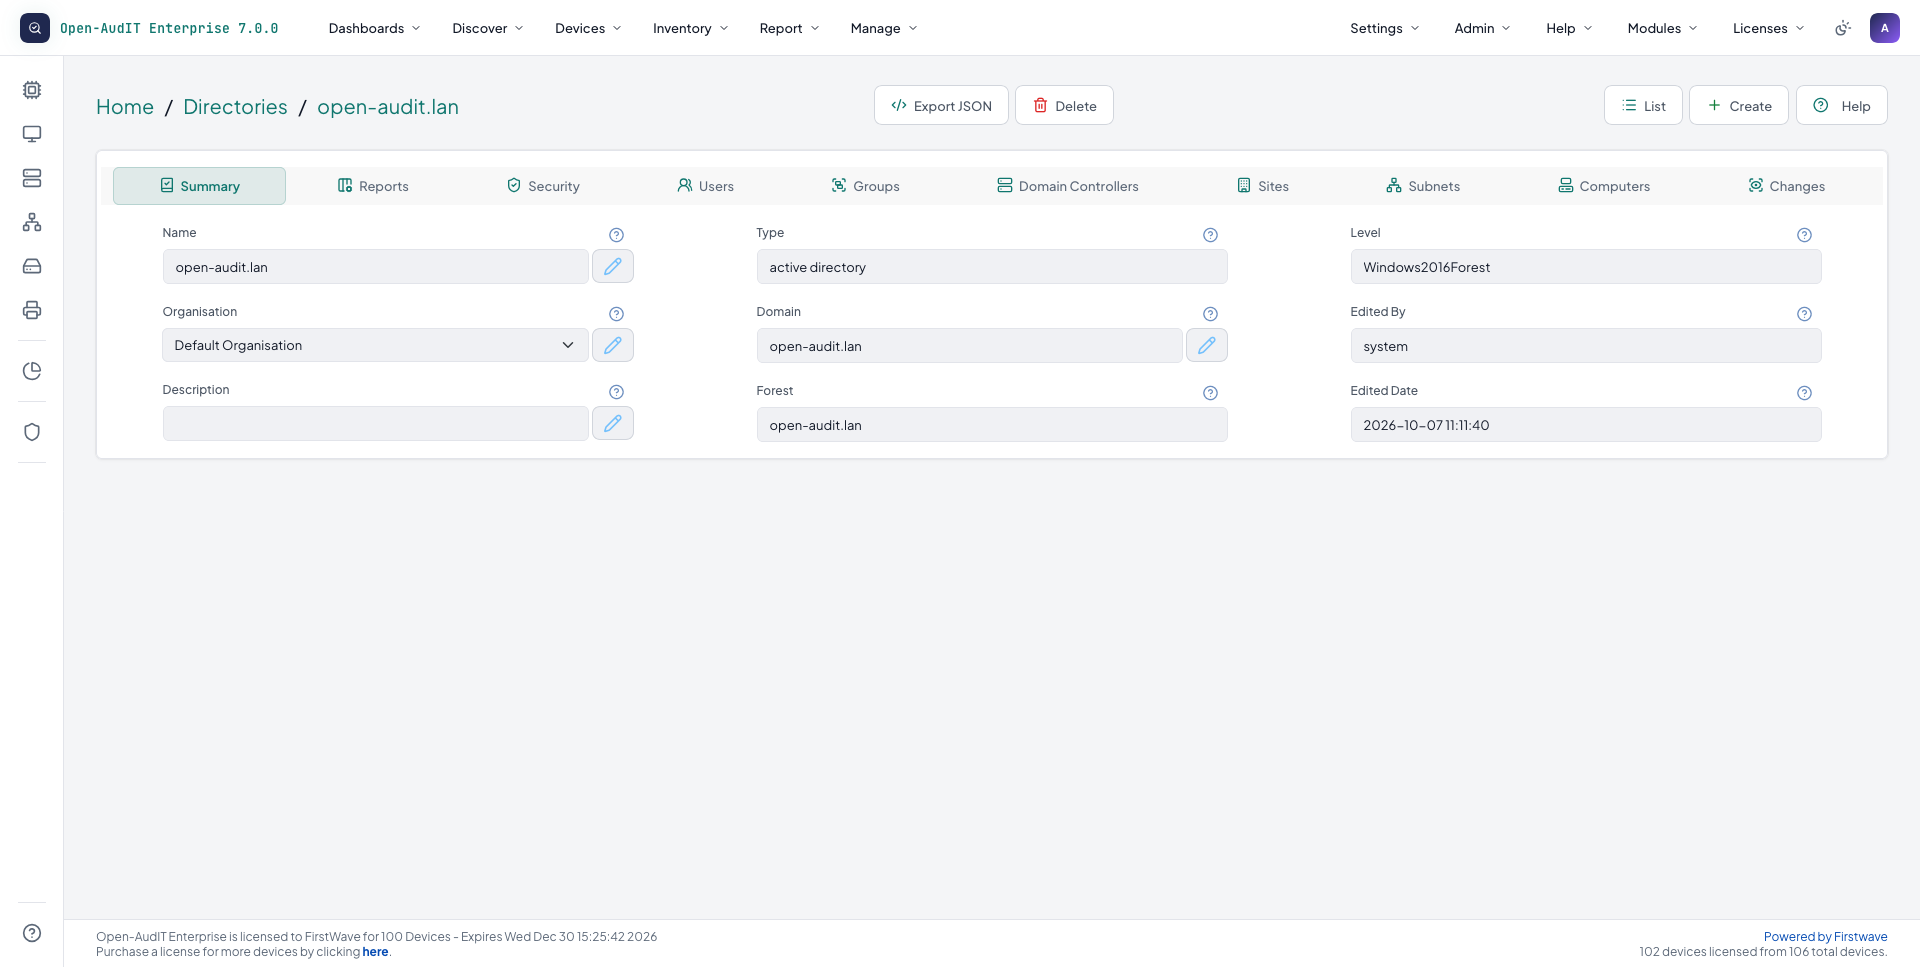
The accounts auditors ask about are flagged for you: not logged on for 30 days, passwords set never to expire, privileged groups that changed this week. Every directory user is linked to the devices they use, and the directory itself is benchmarked against the DISA STIGs.
353 device types classified, up from 98
1,304 compliance controls across five standards
30 days of full Enterprise, unlimited devices
One open port, one reply, one record
Version 7 is built around discovery. Every identification comes from what the device itself said, and Open-AudIT keeps what it said. Step through how one helper reads one port.
1. Scan: Open-AudIT scans the target address. 2. Port check: A helper only runs when its port is open, so nothing is probed speculatively. A network of Windows machines never sees a PLC probe. 3. Helper: The matching helper speaks the device's own protocol and identifies it from the reply. 4. Evidence: The full parsed response is kept as JSON, so the evidence for every identification is one click away.
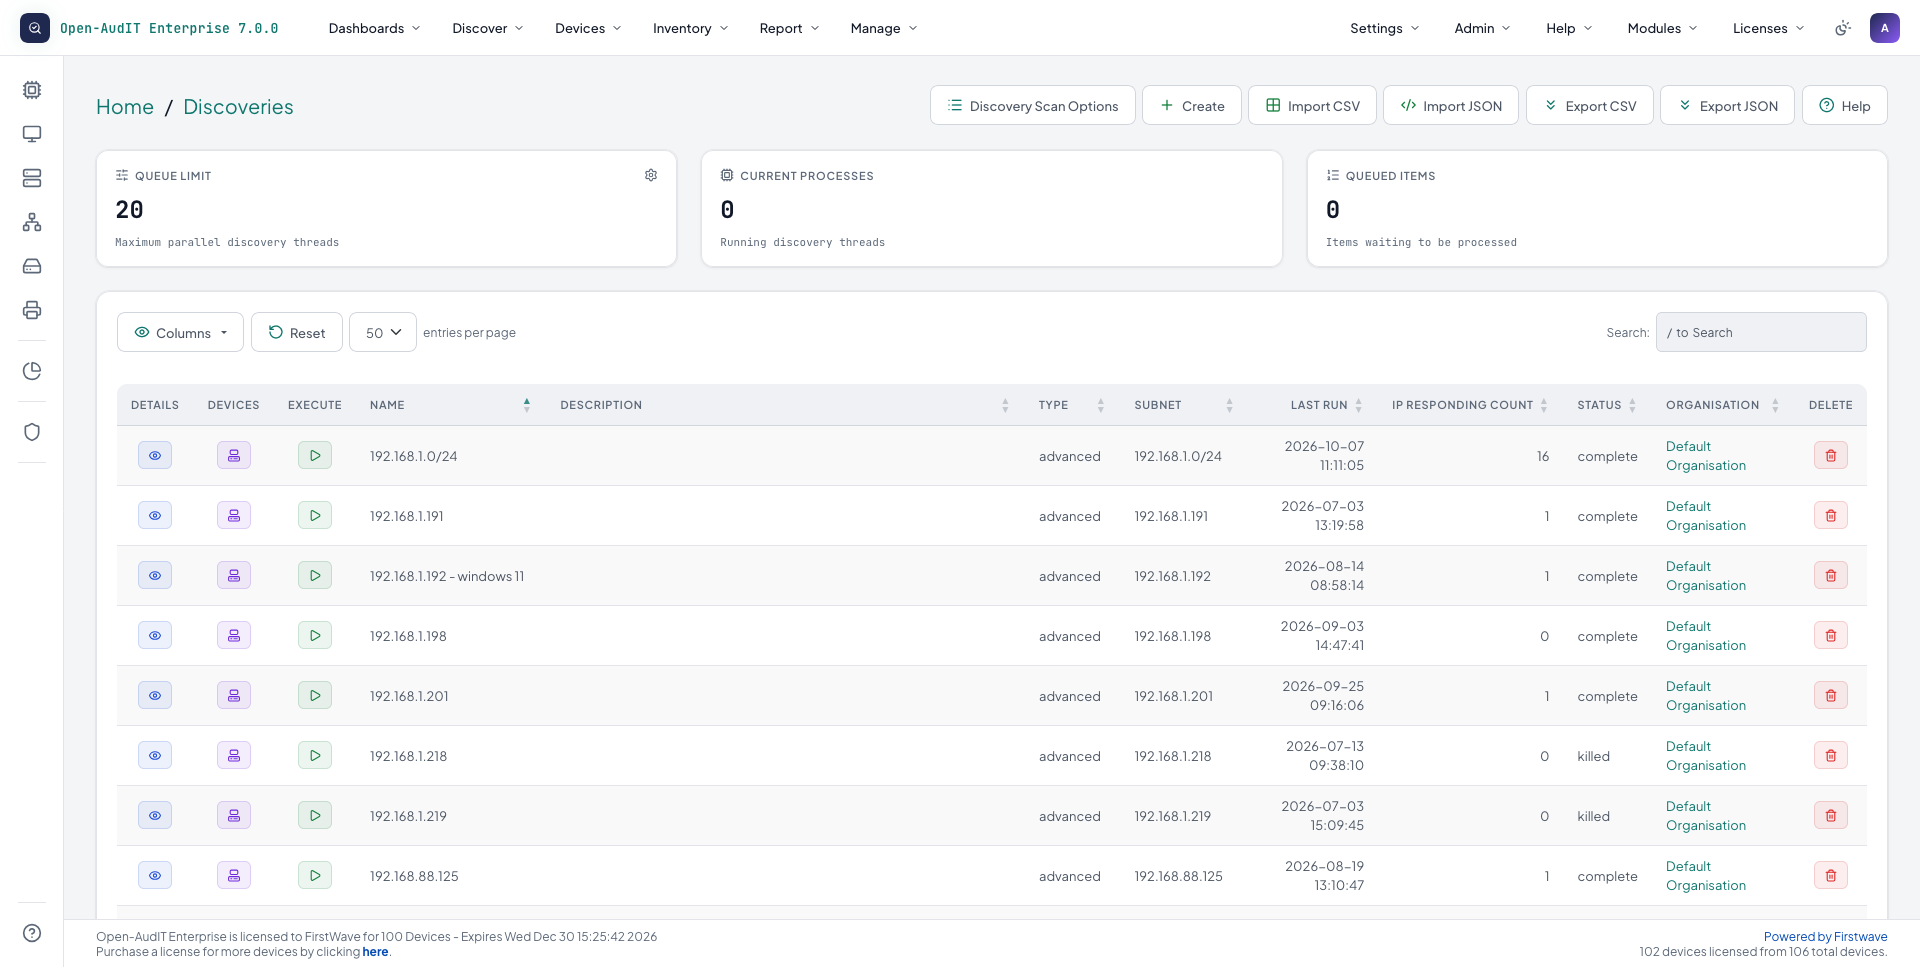
Open-AudIT 7.0.0·Discoveries
Every discovery with its subnet, last run, responding IP count and status, under the discovery queue.
It reaches further than the scan
If it is connected to the network and uses TCP/IP, something has to know it is there.
Subnet splitting
Large ranges are split into smaller subnets and scanned in parallel.
Expanded port coverage
The port list has grown across both TCP and UDP.
ARP discovery
The server's own ARP table is read, and every in-range address in an audited switch, router or computer is queued for its own scan.
Directory targets Enterprise
Active Directory networks and locations can be used as discovery targets.
Collectors on Windows Enterprise
Collectors now run on Windows as well.
The credentialed audit is all still here
Credential-free identification tells you what a device is. A credentialed audit reads what is on it, and its switch and router tables feed ARP discovery and the network map.
Credentialed audit methods carried forward from Version 6
Method
Reaches
SNMP
switches, routers, printers and UPS
SSH
Linux, Unix and network devices
WinRM, winexe / psexec, WMI, SSH
Windows
Then it draws the picture
On Enterprise, what discovery found becomes the network drawn as it is, applications modelled from their real components, and your directory on one screen.
Network Dependency Mapping Enterprise
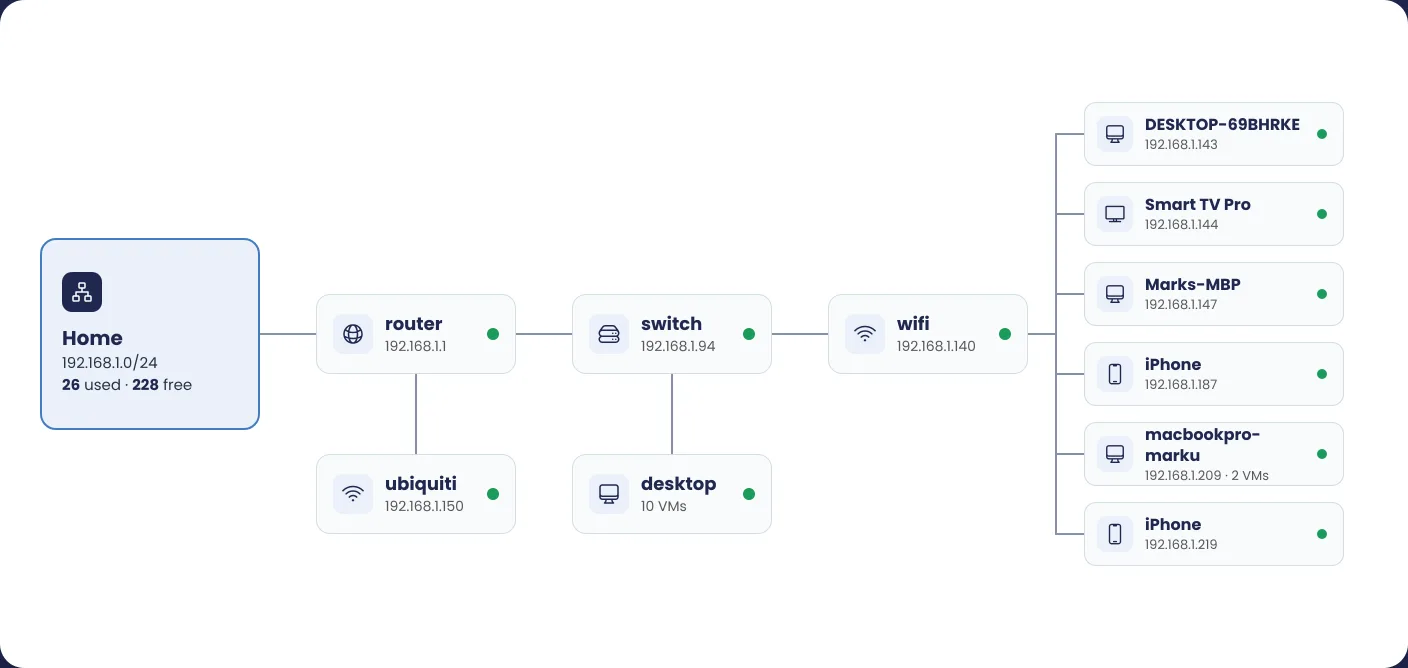
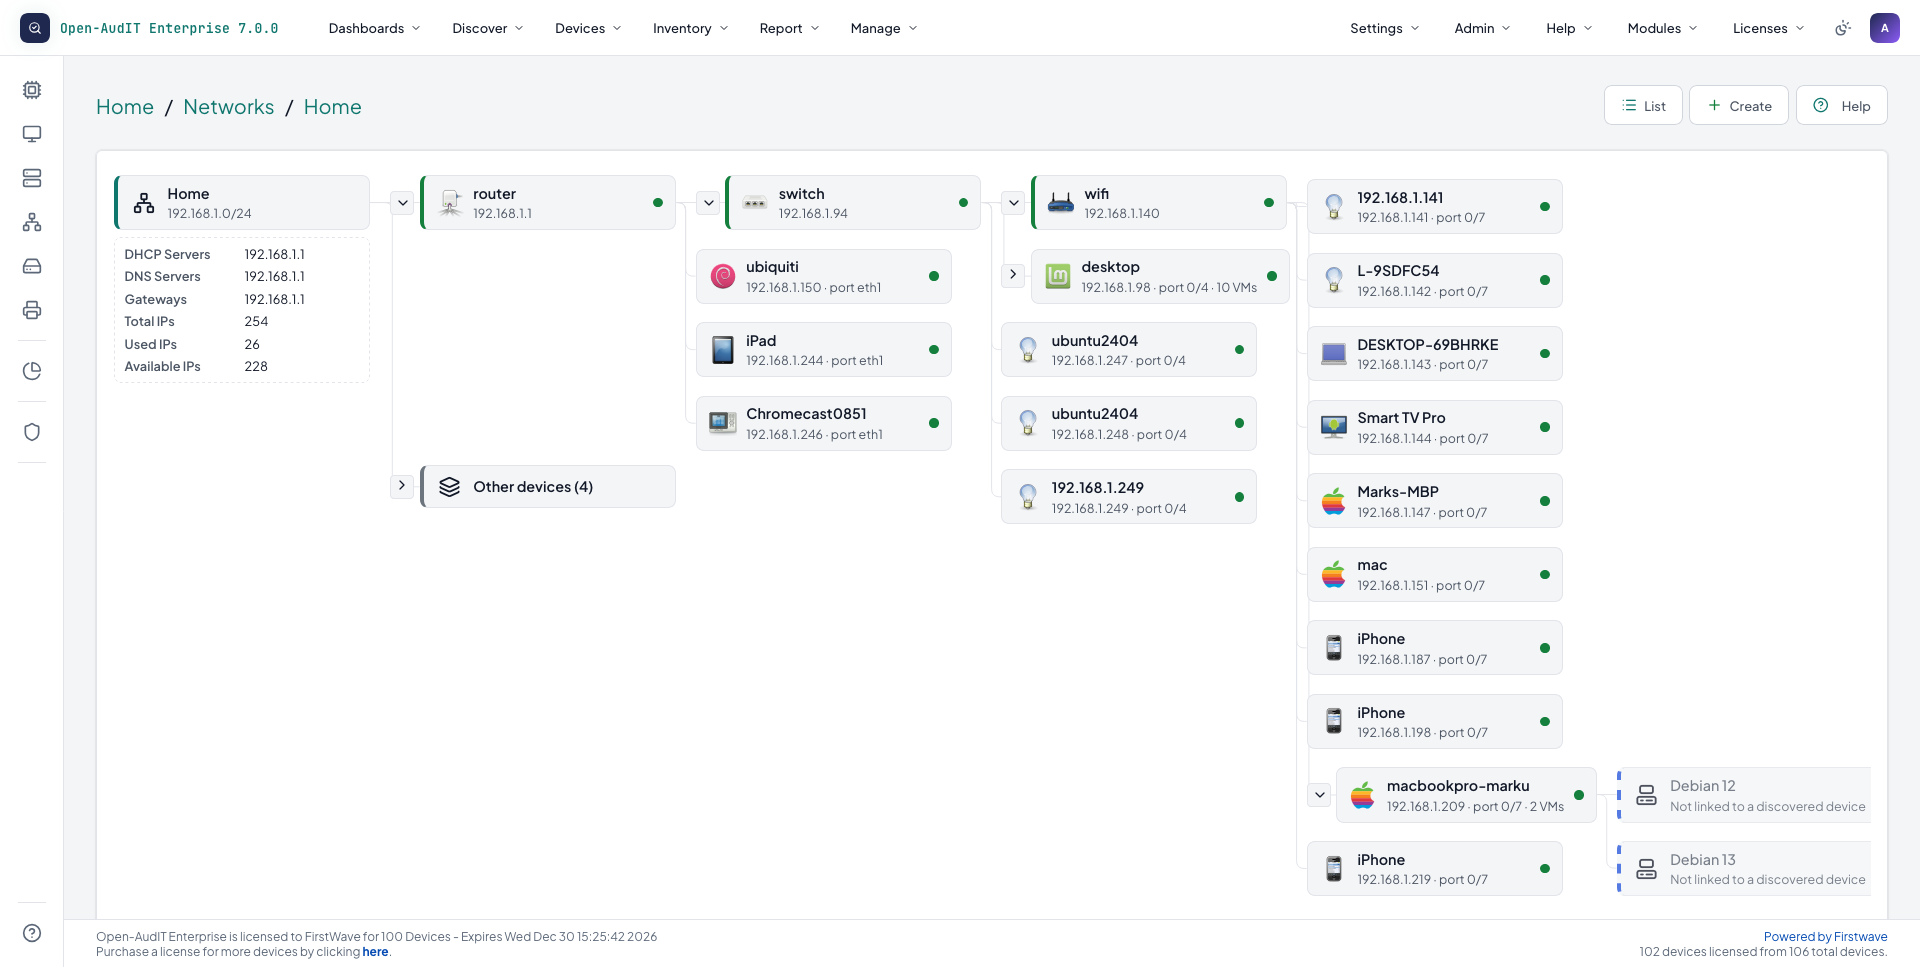
Pick a subnet and see the whole chain, router to switch to wifi to every device.
Each device on the map shows its name, address, connected port and status, with the network's DHCP, DNS, gateway and IP counts alongside.
The map is built from what discovery and your credentialed audits of the network gear learned, so the more completely your switches are audited, the truer the drawing.
Open-AudIT 7.0.0·Networks
One subnet drawn router to switch to wifi to every device, each with its address and port, beside the network's DHCP, DNS, gateway and IP counts.
Application Relationship Mapping Enterprise
Model an application as its real, discovered components.
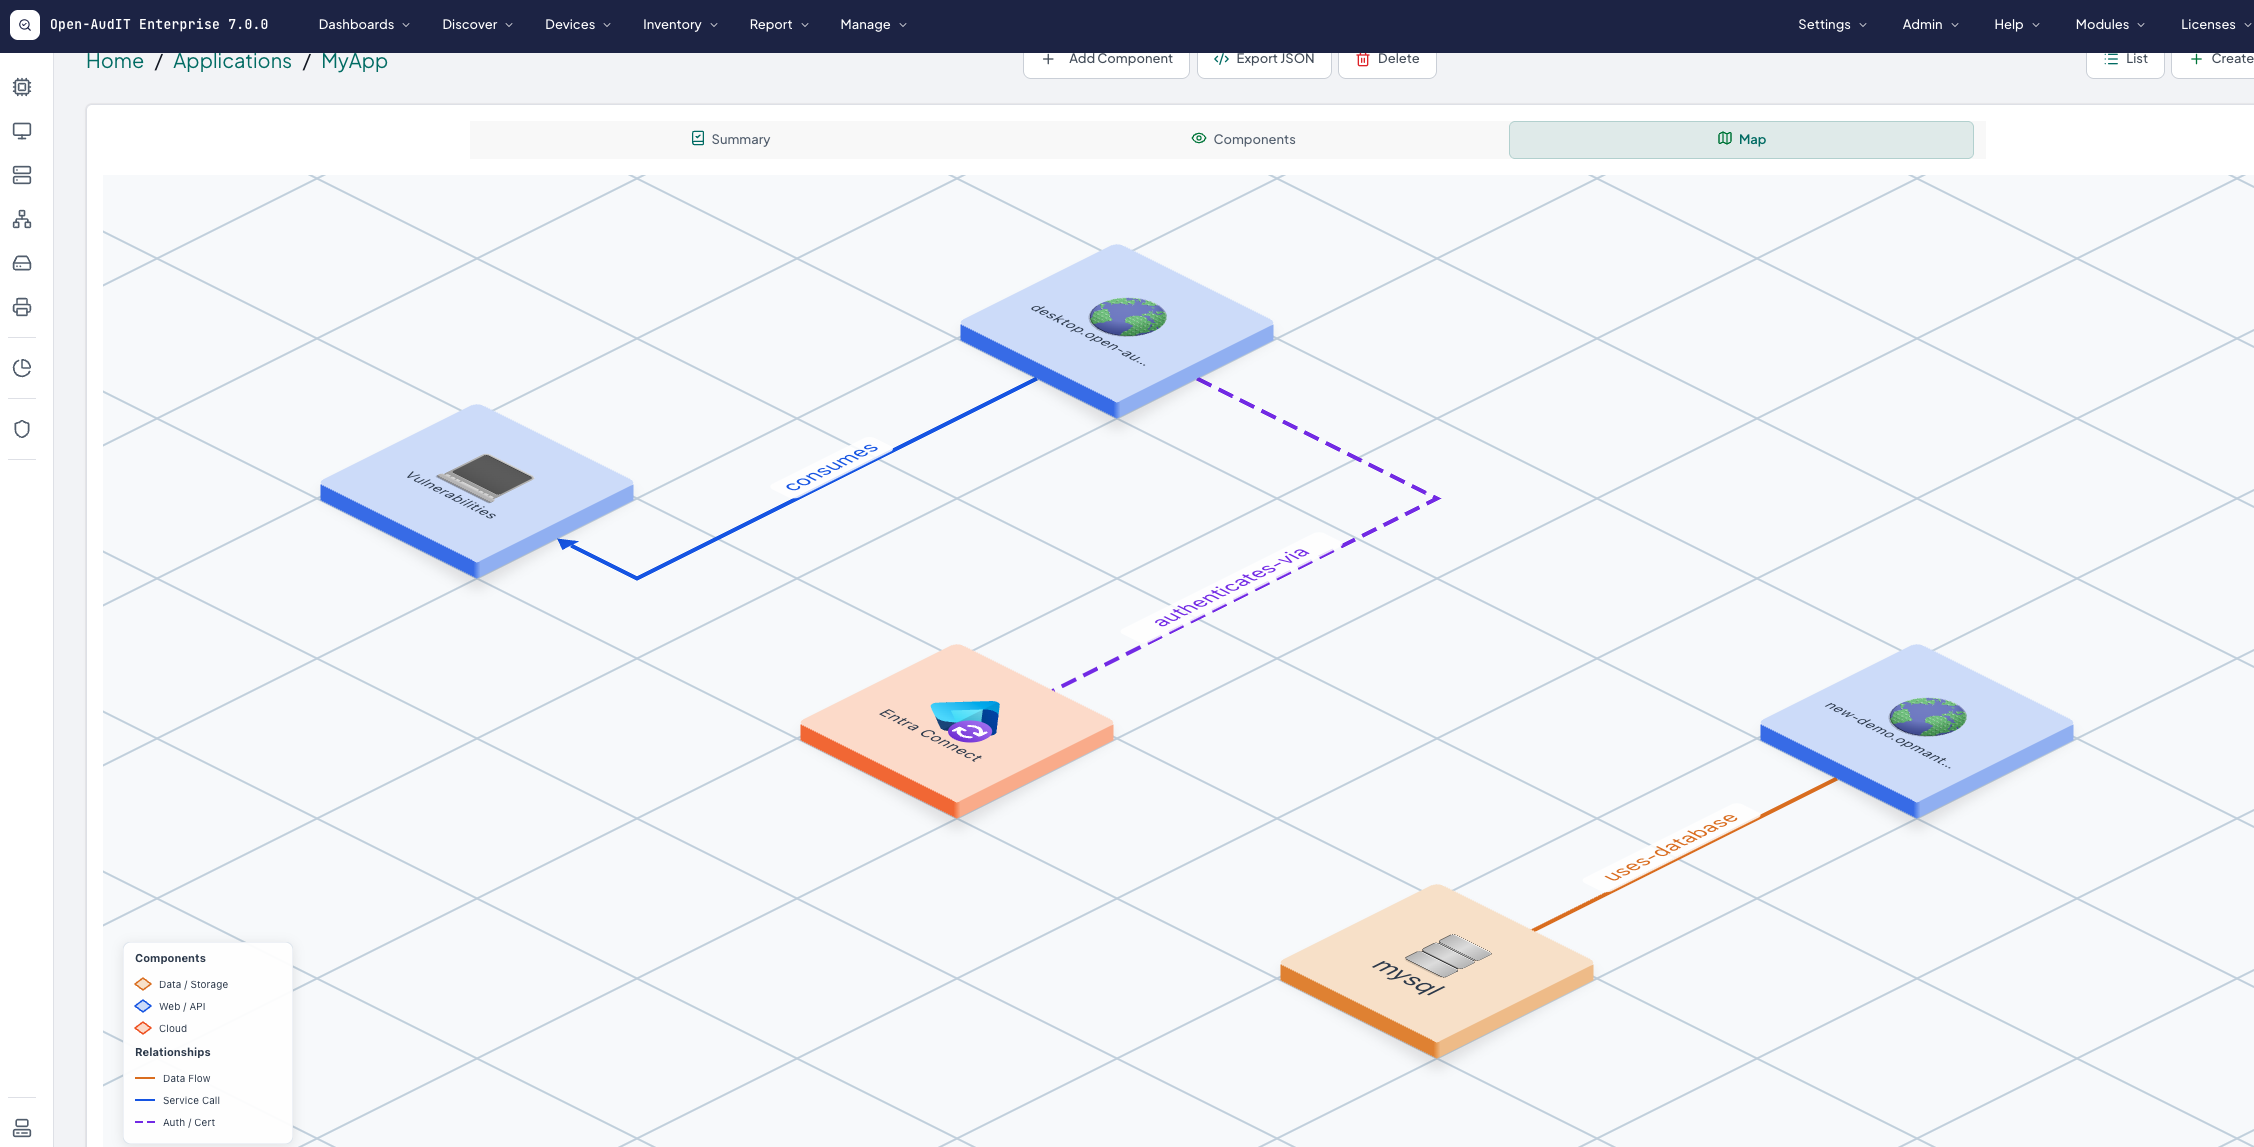
An application is never just one server. Model each one as its components. That means the website, the API behind it, the database it reads and the cloud services it sits on. Each relationship gets a plain name, such as runs-on, uses-database or uses-certificate.
Open-AudIT only offers discovered, available servers and their related databases, so there is no free-text guesswork. A search across every component answers "which applications does this server carry?" before the change window.
Open-AudIT 7.0.0·Applications
An application mapped as its components, each relationship named: consumes, authenticates-via, uses-database.
Directories Enterprise
Users, groups, computers, domain controllers, sites and subnets on one screen, with change history.
Point Open-AudIT at Active Directory and it reads users, groups, computers, domain controllers, sites and subnets, then keeps a history as they change. Entra is supported as well.
The summary tracks accounts not logged on for more than thirty days, passwords set never to expire, group membership changes in the last seven days, and who is in Administrators, Domain Admins and Enterprise Admins.
Open-AudIT 7.0.0·Directories
An Active Directory domain's summary, with tabs for its users, groups, domain controllers, sites, subnets, computers and changes.
Then prove it's configured the way it should be
Enterprise
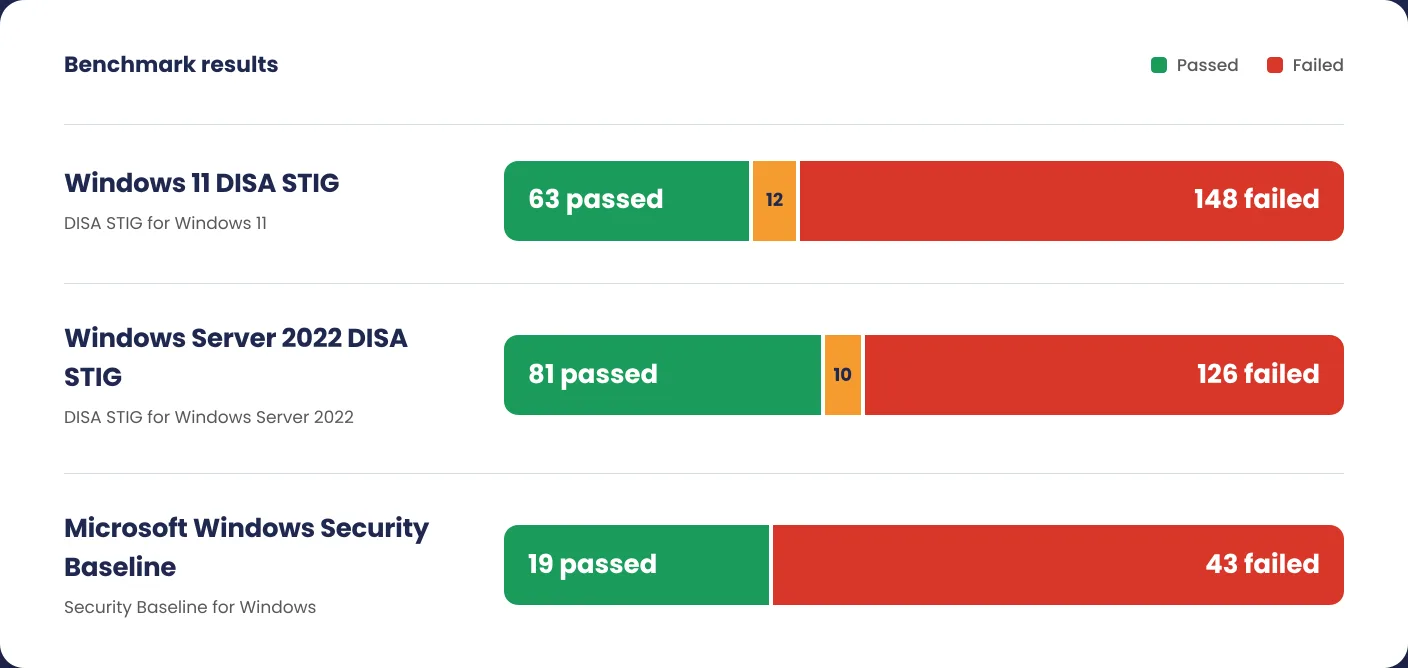
Discovery tells you what is on the network. Benchmarks tell you whether each machine is configured to a published standard, graded by severity and marked pass or fail, with the evidence kept.
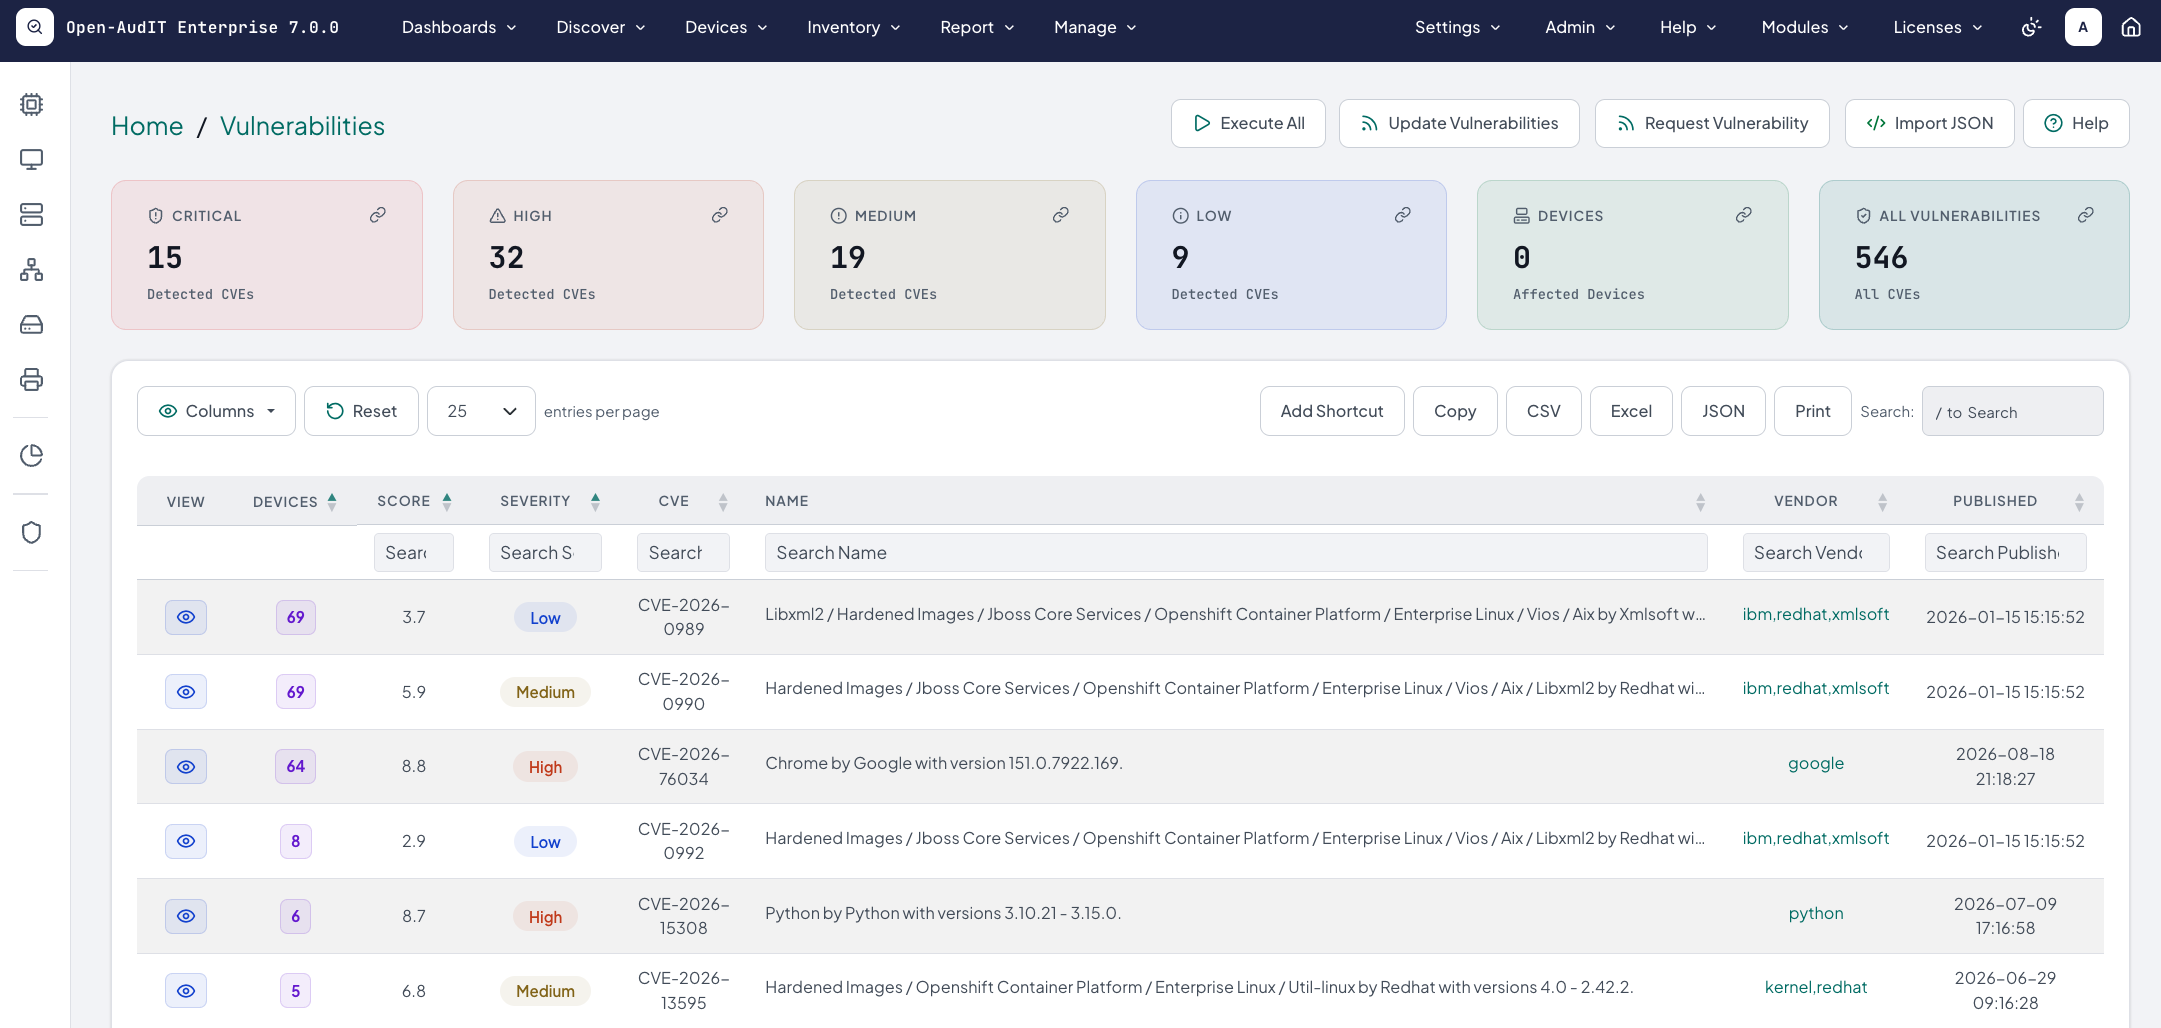
Vulnerability detection, on Professional and Enterprise, carries forward from Version 6. It uses AI to match CVEs to the devices you have discovered and alert you to the ones that affect you.
Linux servers
Profiles include CIS Benchmarks, DISA STIG, NIST 800-171, ACSC Essential Eight, ACSC ISM, HIPAA, PCI-DSS v4.0 and ANSSI, run over SSH with working SSH credentials.
Supported systems are Red Hat Enterprise Linux 7, 8 and 9, CentOS 7, Debian 12, SLES 15 and Ubuntu 20.04 and 22.04. The profiles available vary by distribution.
Windows
DISA STIG checks run as part of a normal audit, with nothing extra to configure.
Standards reporting
Track your performance against ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials, 1,304 controls in all.
Open-AudIT 7.0.0·Benchmarks
Windows 11 and Windows Server 2022 DISA STIG benchmarks and the Microsoft Windows Security Baseline, with passed and failed checks for each.
Domains, vendors and certificates, kept in one place
DomainsEnterprise
Each domain records who it is registered through, the certificate securing it, when it expires and when renewal work should start, with a status of Active, Due For Renewal or Expired.
VendorsEnterprise
Vendors used to be a list of software vendors for filtering vulnerability retrieval. It is now a register of contact, legal and payment details, linked to the things each vendor supplies, and domains link to their registrar.
Certificates matched to web serversEnterprise
Certificates record issuer and fingerprint. Open-AudIT matches them to the web servers using them, by serial from the device audit, and marks a certificate active while any device still uses it.
What you'll use it for every day
Discovery finds the devices. These keep the inventory useful after that, each marked with the edition that includes it.
Inventory
Software and licencesEvery edition
See what software is deployed and how many licences you hold.
Device managementEvery edition
Record who has each device, where it is and its warranty.
Change and drift
Change detectionEvery edition
Every change to a device's attributes is recorded and reported.
Every edition discovers and audits over the network. Enterprise adds agents that audit Windows machines on a schedule without remote access.
Role-based accessEnterprise
Create roles to suit your requirements, including through Active Directory and LDAP.
Start free, grow into the edition you need
Credential-free discovery is in every edition, including Free on up to 100 devices. Professional adds automation, vulnerability detection and commercial support. Enterprise adds mapping, directories and benchmarking.
Which edition fits?
Enter how many devices you expect discovery to find, tick what you need, and the matching edition is marked below.
Free
$0
After your 30-day Enterprise trial, keep going free on up to 100 devices.
Enterprise · free for your first 30 days. No device cap. When the 30 days end, buy a licence, ask us for an extension or move to Free. Activation asks for your email address. Privacy policy
Up to 100 devices
Credential-free discovery engine
OT, IoT and service processor identification
353 device types
Credentialed audits over SNMP, WMI and SSH
Hardware and software inventory with change detection
The free, professional and enterprise products share a common code base, however, Open-AudIT Professional & Enterprise include additional modules that improve discovery, simplify administration and increase reporting capability. Use the comparison chart below to decide which version best suits your organization's requirements.
View only means the edition can use the items that ship with Open-AudIT, but cannot change them or create its own.
Feature
Free
Professional
Enterprise
Attributes. Set the choices in dropdowns such as device type, status and environment.
Included
Included
Included
Authentication (OpenLDAP, Entra and Okta). Sign users in with their OpenLDAP, Active Directory, Entra or Okta accounts.
Included
Included
Included
Components (database, web server and file share discovery). Find database servers, web servers and file shares, and record how each is configured.
Included
Included
Included
Connections. Record the links between your sites, with provider, speed and cost.
Included
Included
Included
Credentials. Store the logons audits use to collect software, users, serial numbers and disks.
Included
Included
Included
Devices. A record for every device on your network, with more than a hundred attributes each.
Included
Included
Included
Discoveries. Save a network and how to scan it, then find what's on it in one click.
Included
Included
Included
Fields. Add your own device fields, such as an asset tag, warranty expiry or cost centre.
Included
Included
Included
Groups. A saved condition that always lists the devices matching it, such as every Windows server.
Included
Included
Included
JSON API. Access all objects and actions programmatically through a comprehensive RESTful JSON API.
Included
Included
Included
Licenses. Tell Open-AudIT what you bought and it counts the installations against it.
Included
Included
Included
Locations. Assign devices to physical sites, from head office to the data centre.
Included
Included
Included
Networks. Your subnets, kept current by discovery, with used and available addresses.
Included
Included
Included
News. Receive curated feeds on updates, advisories, and product insights relevant to your IT environment.
Included
Included
Included
Orgs. Every item belongs to an organisation, and users only see the orgs they're given.
Included
Included
Included
Queries. Saved, rerunnable reports, with a large set included.
Included
Included
Included
Users. Accounts with roles for what they can do and orgs for whose items they can do it to.
Included
Included
Included
Summaries. Reports that count devices by type, operating system or location, each line linked to the devices.
View only
Included
Included
Widgets. The chart and count tiles dashboards are built from. Open-AudIT ships with 87.
View only
Included
Included
Clusters. Record devices that only make sense together, such as database nodes or a firewall pair.
Not included
Included
Included
Commercial Queries
Not included
Included
Included
Maps. Locations with coordinates on an interactive world map, with a device count for each.
Not included
Included
Included
Tasks (scheduling). Run discoveries, queries and cloud audits on a schedule.
Not included
Included
Included
Vulnerabilities. AI matches CVEs to the devices you have discovered and alerts you, with reports showing affected devices and risk severity.
Not included
Included
Included
Agents. Software for Windows machines that are hard to audit. It checks in daily and audits itself.
Not included
View only
Included
Applications. Model each application as its discovered components and the named relationships between them.
Not included
View only
Included
Dashboards. A grid of widgets showing the state of your estate at a glance.
Not included
View only
Included
Discovery Scan Options. Named sets of scan settings, such as which ports to try and how long to wait.
View only
View only
Included
Packages. Approve or ban software packages and find shadow IT.
View only
View only
Included
People. People from your directory, linked to the devices they use.
View only
View only
Included
Roles. Create, read, update and delete permissions for each part of the application.
View only
View only
Included
Rules. If this, then that for devices. When a device matches, other attributes are set.
View only
View only
Included
Baselines. Define expected configurations and compare devices against a baseline.
Not included
Not included
Included
Benchmarks. Check machines against published hardening guides, including the DISA STIGs and CIS Benchmarks.
Not included
Not included
Included
Certificates. Monitor SSL/TLS certificates and their expiry, with issuer and fingerprint recorded and each certificate matched to the web servers using it.
Not included
Not included
Included
Clouds. Discover and audit instances on AWS, Azure and Google Cloud.
Not included
Not included
Included
Collectors. Deploy lightweight collectors to perform secure discovery across remote networks or isolated segments.
Not included
Not included
Included
Directories. Users, groups, computers, domain controllers, sites and subnets on one screen, with change history.
Not included
Not included
Included
Domains. Track registered domain names, their registrar, certificate, expiry and renewal.
Not included
Not included
Included
Files. Watch the files that matter, such as the sudoers or SSH config, and see when they change.
Not included
Not included
Included
Integrations. Share your device list with other systems, such as your monitoring platform.
Not included
Not included
Included
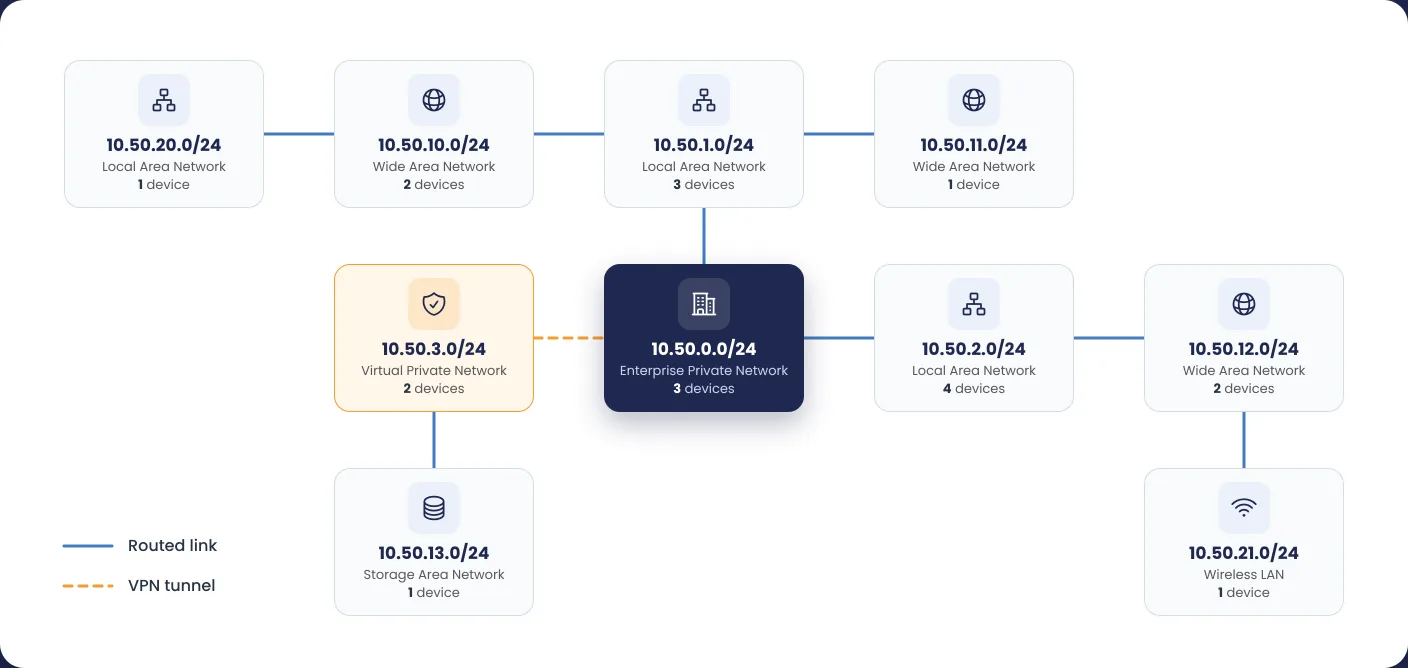
Network Mapping. See each network drawn from router to switch to device, and how your networks connect through routed links and VPN tunnels.
Not included
Not included
Included
Racks. Document racks, RU positions and device placements, and generate rack-level reports.
Not included
Not included
Included
Standards. Generate reports aligned to ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials controls to simplify compliance tracking and audit readiness.
Not included
Not included
Included
Vendors. A register of the companies you buy from, with contact, legal and payment details, linked to what each supplies.
Not included
Not included
Included
Commercial Support. Access vendor support, knowledge and maintenance services.
Not included
Included
Included
Licensed devices. Licensed device volume included with each edition.
Up to 100 Devices
From 100 Devices
From 100 Devices
Attributes
Set the choices in dropdowns such as device type, status and environment.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Authentication (OpenLDAP, Entra and Okta)
Sign users in with their OpenLDAP, Active Directory, Entra or Okta accounts.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Components (database, web server and file share discovery)
Find database servers, web servers and file shares, and record how each is configured.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Connections
Record the links between your sites, with provider, speed and cost.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Credentials
Store the logons audits use to collect software, users, serial numbers and disks.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Devices
A record for every device on your network, with more than a hundred attributes each.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Discoveries
Save a network and how to scan it, then find what's on it in one click.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Fields
Add your own device fields, such as an asset tag, warranty expiry or cost centre.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Groups
A saved condition that always lists the devices matching it, such as every Windows server.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
JSON API
Access all objects and actions programmatically through a comprehensive RESTful JSON API.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Licenses
Tell Open-AudIT what you bought and it counts the installations against it.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Locations
Assign devices to physical sites, from head office to the data centre.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Networks
Your subnets, kept current by discovery, with used and available addresses.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
News
Receive curated feeds on updates, advisories, and product insights relevant to your IT environment.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Orgs
Every item belongs to an organisation, and users only see the orgs they're given.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Queries
Saved, rerunnable reports, with a large set included.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Users
Accounts with roles for what they can do and orgs for whose items they can do it to.
FreeIncluded
ProfessionalIncluded
EnterpriseIncluded
Summaries
Reports that count devices by type, operating system or location, each line linked to the devices.
FreeView only
ProfessionalIncluded
EnterpriseIncluded
Widgets
The chart and count tiles dashboards are built from. Open-AudIT ships with 87.
FreeView only
ProfessionalIncluded
EnterpriseIncluded
Clusters
Record devices that only make sense together, such as database nodes or a firewall pair.
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Commercial Queries
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Maps
Locations with coordinates on an interactive world map, with a device count for each.
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Tasks (scheduling)
Run discoveries, queries and cloud audits on a schedule.
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Vulnerabilities
AI matches CVEs to the devices you have discovered and alerts you, with reports showing affected devices and risk severity.
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Agents
Software for Windows machines that are hard to audit. It checks in daily and audits itself.
FreeNot included
ProfessionalView only
EnterpriseIncluded
Applications
Model each application as its discovered components and the named relationships between them.
FreeNot included
ProfessionalView only
EnterpriseIncluded
Dashboards
A grid of widgets showing the state of your estate at a glance.
FreeNot included
ProfessionalView only
EnterpriseIncluded
Discovery Scan Options
Named sets of scan settings, such as which ports to try and how long to wait.
FreeView only
ProfessionalView only
EnterpriseIncluded
Packages
Approve or ban software packages and find shadow IT.
FreeView only
ProfessionalView only
EnterpriseIncluded
People
People from your directory, linked to the devices they use.
FreeView only
ProfessionalView only
EnterpriseIncluded
Roles
Create, read, update and delete permissions for each part of the application.
FreeView only
ProfessionalView only
EnterpriseIncluded
Rules
If this, then that for devices. When a device matches, other attributes are set.
FreeView only
ProfessionalView only
EnterpriseIncluded
Baselines
Define expected configurations and compare devices against a baseline.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Benchmarks
Check machines against published hardening guides, including the DISA STIGs and CIS Benchmarks.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Certificates
Monitor SSL/TLS certificates and their expiry, with issuer and fingerprint recorded and each certificate matched to the web servers using it.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Clouds
Discover and audit instances on AWS, Azure and Google Cloud.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Collectors
Deploy lightweight collectors to perform secure discovery across remote networks or isolated segments.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Directories
Users, groups, computers, domain controllers, sites and subnets on one screen, with change history.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Domains
Track registered domain names, their registrar, certificate, expiry and renewal.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Files
Watch the files that matter, such as the sudoers or SSH config, and see when they change.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Integrations
Share your device list with other systems, such as your monitoring platform.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Network Mapping
See each network drawn from router to switch to device, and how your networks connect through routed links and VPN tunnels.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Racks
Document racks, RU positions and device placements, and generate rack-level reports.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Standards
Generate reports aligned to ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials controls to simplify compliance tracking and audit readiness.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Vendors
A register of the companies you buy from, with contact, legal and payment details, linked to what each supplies.
FreeNot included
ProfessionalNot included
EnterpriseIncluded
Commercial Support
Access vendor support, knowledge and maintenance services.
FreeNot included
ProfessionalIncluded
EnterpriseIncluded
Licensed devices
Licensed device volume included with each edition.
Open-AudIT tells you what is on your network, how each device is configured and when that changes. It runs on a server you control, scans your networks for devices, audits what it finds and stores the results in a database you can query, report on and export. It needs no agent on the devices it audits, though Enterprise offers one for machines you cannot reach remotely.
What is new in Open-AudIT 7?
Version 7 is built around discovery. A new engine identifies devices without credentials, reading what each device's own protocol says back. That covers smart TVs, security cameras, PLCs, building controllers, NAS units and the management controllers inside servers. Enterprise also gains Network Dependency Mapping, the Network Routing Map, Application Relationship Mapping, a Directories view for Active Directory and Entra, Windows benchmarking against the DISA STIGs, and registers for Domains and Vendors. Every edition gets 353 device types (up from 98) and rewritten in-application documentation.
I am on version 6. Do I need to start again?
No. Open-AudIT 7.0.0 upgrades in place from any supported 6.x release, and everything customers rely on in version 6 carries forward. Upgrading also starts the 30-day Enterprise trial. Run the new installer, log in, and you will be taken to the database schema upgrade screen. Take a database backup first. The ip table is renamed to ip_address, but a view named ip is created so existing reports and integrations that read it keep working.
Discovery and credentials
Does Open-AudIT need credentials to discover devices?
Not to identify them. Open-AudIT 7 reads what each device's own protocol says back, and the parsed reply is kept in the discovery log as evidence. Add credentials and it discovers even more, running a full audit over SNMP, SSH, WinRM, WMI, or the APIs of ESXi, Proxmox, Nutanix and XCP-ng hosts.
What is the difference between discovery and an audit?
Discovery tells you what a device is. An audit reads what is on it. Open-AudIT first checks each target address for open ports, then runs a helper only where its port is open, so nothing is probed speculatively. If you hold working credentials for a computer, an audit script is copied to it and run, returning hardware, software and configuration detail. Switches, routers, printers and UPS units are queried over SNMP instead. Without credentials you still get a record of the device and whatever its open ports revealed.
What kinds of devices can it identify without a login?
The credential-free helpers cover PLCs over protocols such as S7, building management over BACnet and KNX, security cameras and recorders, including over ONVIF, server management controllers over Redfish, IPMI and Intel AMT, NAS units, printers, UPS, VoIP phones, smart TVs and media devices, game consoles, smart plugs and lights, access control terminals, fuel tank gauges, solar inverters, and specialist and unmanaged equipment. A device that answers nothing else usually presents a TLS certificate that names its vendor, and Open-AudIT reads that too.
What credentials do I need for a full audit?
Windows needs an account with administrator rights on the target, with a password set. On a domain, that is a member of the target's Administrators group. Off a domain, it is the built-in Administrator account, or another administrator with a registry change described in the documentation. Linux, Unix and macOS are audited over SSH and need root or sudo to retrieve every attribute. Network gear needs SNMP read access, and v1, v2c and v3 are all supported.
Does it need agents?
No. Every edition discovers and audits over the network. Enterprise adds optional agents, which are simple scripts that check in with the server each day and audit the machine locally, for Windows, macOS and Linux machines you would rather not open to remote access.
Can it discover a large or segmented network?
Yes. Version 7 splits large ranges into smaller subnets and scans them in parallel, reads the server's own ARP table, and queues every in-range address found in the tables of an audited switch, router or computer for its own scan. On Enterprise, Active Directory networks and locations can be used as discovery targets, and Collectors run on a remote subnet under the control of a central server, on Linux or Windows.
Installing and running it
What does it run on?
A 64-bit server, physical or virtual. Supported operating systems are Red Hat 9 and 10, Debian 12 and 13, Ubuntu 24.04, and Windows Server 2016 and later. Windows 10 and 11 are not supported as the server, because the desktop TCP/IP stack throttles the outbound connections discovery relies on. Open-AudIT is also included in the FirstWave VM if you would rather not install anything.
What hardware do I need?
For a responsive install the documentation recommends at least an Intel i7 class CPU, 16 GB of memory, 40 GB of disk and an SSD. It will install and run on anything that can run Apache and MySQL, just more slowly. Memory and fast disk make the biggest difference, because the database does most of the work. Vulnerability detection adds load, as it runs around 20,000 SQL statements at the end of each discovery.
How long does it take to get going?
Under ten minutes from download to first discovery, according to the install guides. The installer handles every dependency on Linux and Windows, so there is nothing to install first. On Windows, set the Apache service to run as a regular user account so it can reach network resources. Then log in, activate your licence, add credentials, add a discovery and run it.
Does Open-AudIT need internet access?
Only for two optional features. Vulnerability detection downloads CVE-derived definitions from FirstWave, and News delivers product updates and one-click configuration recommendations. Both send a small, documented set of non-sensitive data back (licence and application details, error logs, and counts of device types and features used, with no IP addresses, OS versions or software names). Both can be disabled, and the Help icon on the Vulnerabilities page shows exactly what is sent. Discovery and auditing run entirely inside your network.
Editions, licensing and support
What is the difference between Free, Professional and Enterprise?
Every edition includes discovery, credentialed auditing, change detection, software licence reporting, device management, custom fields, export to CSV, XML and JSON, and the JSON API. Professional adds scheduling of discoveries and reports, dashboards, vulnerability detection, reporting over a date range, geographical maps and commercial support. Enterprise adds network and application mapping, directories and people, benchmarking, standards reporting, baselines, file change detection, agents, collectors, cloud auditing, role-based access control, Entra and Okta sign-in, rules and custom dashboard widgets. Compare the editions on this page.
How does the licence work?
Every download of Open-AudIT 7 starts with a 30-day Enterprise licence covering unlimited devices, so you work with the full product from day one. Activation asks for your email address. When the trial ends you can buy a licence, ask FirstWave's sales team for an extension, or move to the Free edition, which covers up to 100 devices. Open-AudIT discovers over the network, so the device count is the number of devices in your inventory, not the number of users.
What support do I get?
Free users have the community documentation and forums. Professional and Enterprise include commercial support from the people who build the product. When you open a ticket, attach the Install Support file from the Support page in the application, plus the Discovery Support export if the issue is with discovery. Those two files let support see how your server is running without a round of back-and-forth questions.
How do I log in for the first time?
Browse to http://<your server>/open-audit/index.php/ (on Windows there are also Start Menu entries). A default administrator account is created at install, and its credentials are listed on the Open-AudIT FAQ page in the documentation. Change that password straight after your first login, then add your own users under Manage, Users.
Compliance, data and integrations
What does Open-AudIT benchmark against?
Benchmarking checks whether a machine is configured to a published standard, graded by severity and marked pass or fail. On Enterprise, Linux servers are checked over SSH using OpenSCAP profiles, and Windows machines get DISA STIG results as part of a normal audit with nothing extra to configure. Windows coverage is Windows 10 and 11, Windows Server 2019, 2022 and 2025, and the Microsoft Windows Security Baseline. Active Directory is also benchmarked against the DISA STIGs, in the Security view on the directory's page.
Can it help with ISO 27001 or other regulatory standards?
Yes, on Enterprise. Standards reporting records your answer and evidence against each control and reports completion, with an Excel export for auditors. ISO 27001 ships with 93 controls. Version 7 adds four more control sets, loaded and ready: CBDDO (660 controls) and BDDK (319) for Türkiye, NCA ECC (174) for Saudi Arabia, and ASD Essentials for Australia. Together the five standards provide 1,304 controls.
Can I get my data out, or feed another system?
Yes. Every list exports to CSV, XML or JSON, and the database structure is open and documented. A RESTful JSON API supports create, read, update and delete on every collection, including the six new ones in version 7 (directories, groups, directory security, directory changes, domains and people), which is how customers feed a CMDB. On Linux, Enterprise can also log new devices, component changes and vulnerabilities to syslog in Common Event Format for tools such as Splunk.
Is Open-AudIT an alternative to NetBox?
They serve different primary jobs. Open-AudIT is a discovery-first inventory and audit tool with built-in network scanning, change tracking, benchmarking and vulnerability detection. NetBox is an IPAM and DCIM documentation platform. Many organisations run both.
Does Open-AudIT do IPAM?
Open-AudIT records every IP address it discovers and, in version 7, draws each network with its DHCP, DNS, gateway and IP counts alongside. For dedicated IP address management, FirstWave offers opAddress, an IPAM module integrated with NMIS.
Which languages does the interface support?
Forty-two, including English, Spanish, Portuguese, German, French, Japanese, Chinese and Arabic. Translations are machine-generated, and FirstWave corrects any you report.
Find out what answers on your network.
Download the FirstWave VM and start a discovery. No credit card required.
Enterprise · free for your first 30 days. No device cap. When the 30 days end, buy a licence, ask us for an extension or move to Free. Activation asks for your email address. Privacy policy